CISSP vs CISA vs Security+: Which Security or Audit Certification Fits You
Security+ starts a security career, CISSP is for people who build and lead security, and ISACA CISA is for people who audit it. Formats, fees, experience rules, one real practice question from each, and how to choose.

CISSP, ISACA CISA and CompTIA Security+ are not three options for the same job. Security+ is where a security career starts, CISSP is for people who build and lead security, and ISACA CISA is for people who audit it. Security+ has no experience requirement. CISSP and ISACA CISA both need five years of relevant work before you hold the full credential. Pick by the job you want and the years you have, not by which acronym sounds most senior.
This guide puts all three side by side: format, cost, experience rules, the mindset each exam rewards, one real practice question from each, how they fit an accounting or audit career, and a simple way to decide.
Last updated: September 2026.
Quick takeaways
- Security+ (CompTIA, exam SY0-701) is an entry-level security certification with no experience requirement: up to 90 questions in 90 minutes, 750 on a 100 to 900 scale to pass.
- CISSP (ISC2) is for security leaders and architects: an adaptive exam of 100 to 150 items in up to 3 hours, 700 out of 1000 to pass, plus five years of experience in two or more of eight domains.
- ISACA CISA (Certified Information Systems Auditor) is for IS auditors and GRC professionals: 150 questions in 4 hours, 450 on a 200 to 800 scale to pass, plus five years of IS audit, control, assurance or security experience.
- CISSP tests the risk manager's judgment. ISACA CISA tests the auditor's judgment: evaluate and report, never fix. Security+ tests fundamentals.
- The usual path is Security+ early, then CISSP or ISACA CISA years later, depending on whether you want to build or audit.
- None is a prerequisite for another, but Security+ is on ISC2's list of credentials that can waive one year of CISSP experience.
The three certifications side by side
| Attribute | CompTIA Security+ | CISSP | ISACA CISA |
|---|---|---|---|
| Issuer | CompTIA | ISC2 | ISACA |
| Level | Entry level | Senior, management | Mid to senior, audit |
| Role it fits | Security analyst, sysadmin moving into security | Security architect, engineer, manager | IS auditor, IT audit, GRC, compliance |
| Experience to certify | None | 5 years in 2+ of 8 domains | 5 years in IS audit, control, assurance or security |
| Format | Fixed form, includes performance-based items | Computerized adaptive testing (CAT) | Fixed, multiple choice |
| Questions and time | Up to 90, 90 minutes | 100 to 150, up to 3 hours | 150, 4 hours |
| Passing score | 750 (100 to 900 scale) | 700 out of 1000 | 450 (200 to 800 scale) |
| Domains | 5 | 8 | 5 |
| Exam fee | See CompTIA | $749 (Americas) | $575 members, $760 non-members |
| Core question | Do you know the fundamentals? | What should the security leader do? | What should the auditor do? |
Sources: the ISC2 CISSP exam outline, ISACA's CISA page and CompTIA Security+. Two notes on those numbers. First, both 700 and 450 are scaled scores, not percentages: ISACA CISA's 450 is not "56 percent correct." Second, CompTIA says the next version, Security+ V8, is expected on or around November 17, 2026, so check which exam code you are booking.

What each certification is actually for
Security+ proves the fundamentals. It assumes nothing. A career switcher can learn the material from a standing start: threat types, cryptography basics, access control, secure architecture, security operations and program management. It is the most common first security certification and it satisfies the DoD 8140 baseline for many roles. The details of the format are in our guide to how many questions are on the Security+ exam.
CISSP proves you can build and govern a security program. Its eight domains run from Security and Risk Management (16 percent) to Software Development Security (10 percent). The exam wants the answer a security leader would give, which is usually the most risk-aware, process-correct option rather than the most technical one. That is why strong engineers often fail their first attempt. The full format and domain breakdown is in our CISSP exam guide.
ISACA CISA proves you can audit an information system. Not run it, not secure it, audit it. Its five domains, per ISACA's content outline, are weighted like this:
| ISACA CISA domain | Weight |
|---|---|
| Information Systems Auditing Process | 18% |
| Governance and Management of IT | 18% |
| Information Systems Acquisition, Development and Implementation | 12% |
| Information Systems Operations and Business Resilience | 26% |
| Protection of Information Assets | 26% |
The right answer on ISACA CISA almost always preserves the auditor's independence: gather evidence before concluding, report rather than fix, and never make management's decisions. Our ISACA CISA exam cost guide covers the fees and scoring in more detail.
One real practice question from each exam
The fastest way to feel the difference is to see how each exam asks. All three come verbatim from PrepClubs' question banks.
From PrepClubs CompTIA Security+ Practice Test 2 (SY0-701), question 27:
A hospital wants to ensure that a compromise of one workstation in the front office cannot let an attacker reach the medical imaging systems on the same physical network. Which mitigation technique MOST directly reduces this lateral movement risk?
A. Monitor east-west traffic with an IDS sensor and alerting B. Encrypt the front-office workstation drives with full-disk encryption C. Segment the imaging network into its own zone behind a firewall D. Lengthen password requirements for all front-office accounts
Answer: C. Segmentation puts the imaging systems in their own zone, so a compromised front-office machine has no path to them. An IDS (A) detects lateral movement but does not stop it, disk encryption (B) does nothing while the machine is running, and longer passwords (D) do not help once a workstation is already compromised. This is the Security+ shape: know which control does what.
From PrepClubs CISSP Practice Test 2, question 9:
A retailer is about to grant a new marketing analytics vendor direct query access to its customer database, which contains personal data. The security manager has not yet reviewed the vendor. What should the security manager do FIRST?
A. Require the vendor to encrypt query results in transit B. Perform a third-party risk assessment of the vendor C. Add data processing clauses at the next renewal D. Grant read-only access and monitor vendor queries
Answer: B. Exposing personal data to a third party has to be assessed before it happens. Encryption (A) is one narrow fix chosen before anyone knows the vendor's risk. Waiting for renewal (C) leaves data exposed in the meantime, and monitoring (D) only reacts after the data is already out. This is the CISSP shape: assess before you act, as the person who owns the risk.
From PrepClubs ISACA CISA Practice Test 2, question 59:
A development project team asks the assigned IS auditor to approve each design document so the team can proceed without delay. Why should the auditor decline to give such approvals?
A. Audit charters prohibit auditors from reading design documentation. B. Auditors lack the technical expertise to evaluate system designs. C. Approval work would push the review beyond its agreed audit budget. D. Approving deliverables makes the auditor a decision-maker, impairing independence.
Answer: D. Signing off design deliverables makes the auditor part of management's decisions, so any later review of that work becomes a self-review. The auditor can attend reviews, comment on control design and advise, but approval stays with project management. This is the ISACA CISA shape: protect independence, even when a technically helpful action is on offer.
Same broad topic area, three different instincts. Security+ wants the right control. CISSP wants the right first step for a risk owner. ISACA CISA wants the answer that keeps the auditor independent.
The experience rules, compared
| Security+ | CISSP | ISACA CISA | |
|---|---|---|---|
| Experience to sit the exam | None | None | None |
| Experience to certify | None | 5 years, 2+ domains | 5 years in IS audit, control, assurance or security |
| Waivers | Not applicable | Up to 1 year for a relevant degree or an approved credential | Up to 3 years for certain education and experience |
| If you pass without the experience | Not applicable | Associate of ISC2, 6 years to earn it | Apply within 5 years of passing, with experience from the prior 10 years |
For CISSP, the details are on ISC2's experience requirements page. ISC2 revised its approved waiver list on April 1, 2026, so confirm your credential is still on it. For ISACA CISA, check ISACA's current application terms before you rely on a waiver.
The practical point: CISSP and ISACA CISA are both mid-career credentials. You can sit either exam early to lock it in, but the certificate waits for the years.
Which is harder?
- CISSP is the broadest and the most unforgiving format. Eight domains, an adaptive engine that gets harder as you do well, and no going back to a question. Its real difficulty is the manager mindset.
- ISACA CISA is narrower but counterintuitive. Five domains, but the auditor logic (evaluate and report, never fix) is not how most technical people think. It keeps offering the technically correct action that is the wrong auditor action.
- Security+ is the most approachable, though the performance-based questions catch people out. It is a different order of difficulty from the other two.
If you already think like a security leader, CISSP feels natural. If you already think like an auditor, ISACA CISA does. Neither is a memorization exam.

The ladder most people actually climb
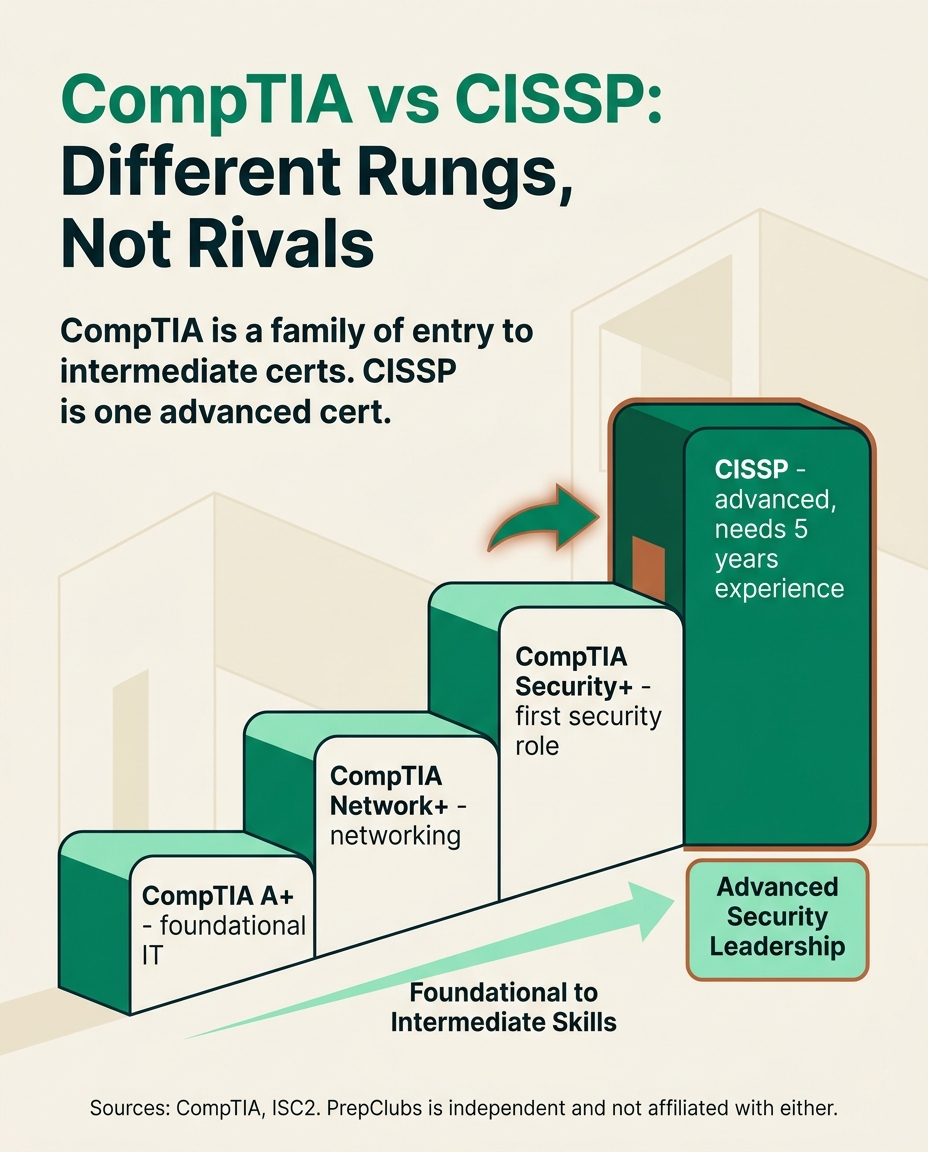
"CompTIA vs CISSP" is a category error: CompTIA publishes a family of certifications, and CISSP is one advanced credential. The comparison people usually mean is Security+ vs CISSP, and those sit at opposite ends of the same path.
- A+ or Network+ for foundational IT and networking. Our CompTIA certifications list shows how they fit together.
- Security+ as your first dedicated security certification.
- Several years of work in security, audit or both.
- CISSP if you are building and leading security, ISACA CISA if you are auditing it. Many senior people eventually hold both.
Take two people asking the same question. A help desk technician with one year of experience should take Security+: CISSP's credential is years away however well she studies, and Security+ gets her the next job now. A security engineer with seven years of experience whose employer wants a security lead should skip Security+ and go for CISSP: he already meets the requirement and needs the management-level credential. Same question, opposite answers, and experience decides it both times.
If you are in accounting or audit
For accountants moving toward systems work, ISACA CISA is the credential IT audit and SOX controls postings name most directly. One naming trap first: CISA is also the abbreviation for the US Cybersecurity and Infrastructure Security Agency, a federal agency that issues advisories, not credentials. Write and search "ISACA CISA" to keep them apart.
| Credential | Issuer | Best fit | Note |
|---|---|---|---|
| ISACA CISA | ISACA | IT audit, SOX controls, systems risk | The one this category orbits |
| CPA, ISC discipline | AICPA and state boards | Licensed accountants wanting a technology track | ISC is a CPA exam section, not a standalone credential |
| CIA | The IIA | Internal audit and enterprise risk | Three parts, scaled 250 to 750, 600 to pass |
| CITP | AICPA | CPAs specializing in technology | Needs a CPA certificate. The exam is waived for ISACA CISA holders |
| CRISC | ISACA | IT risk and control design | A risk credential, not an audit one |
| CISM | ISACA | Security program management | A security leadership credential, closer to CISSP |
| Security+ | CompTIA | Security literacy for career changers | No prerequisite, not an accounting credential |
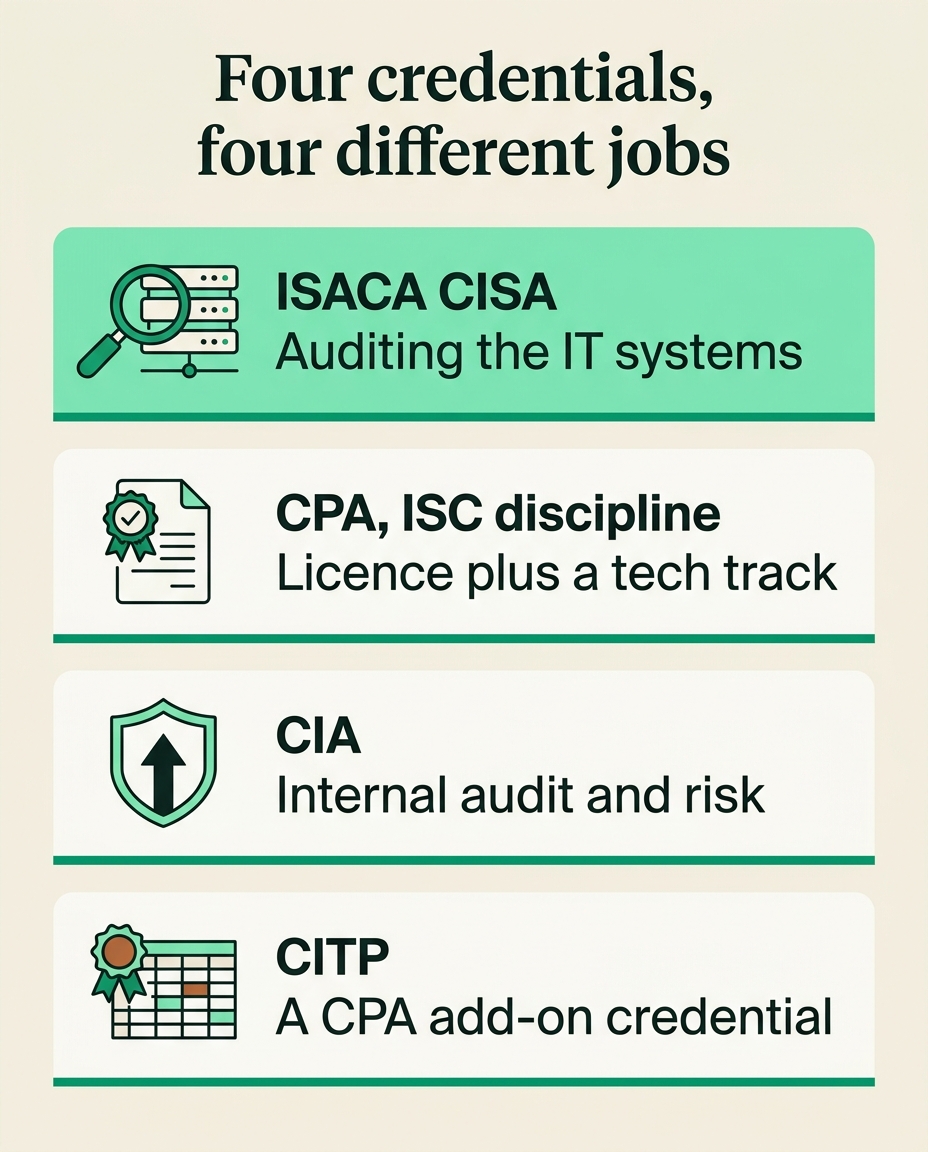
Quick routing for audit careers:
- In audit and moving toward systems: ISACA CISA.
- Already a CPA wanting technology credibility: ISACA CISA first, then the CITP with the exam waived.
- Mid-CPA and choosing a discipline: ISC, if technology and controls work is where you want to land.
- Staying in internal audit: the CIA, with CRISC if your work is risk-heavy.
None of these replaces a CPA licence where attest work legally requires one, and none turns an auditor into an engineer. ISACA CISA proves you can evaluate whether controls work, not that you can build the system.
How to choose in one minute
- Under two years in IT or security, or changing careers: Security+.
- Five or more years, building, defending or leading security: CISSP.
- Five or more years in audit, GRC or compliance: ISACA CISA.
- Close to five years: sit the CISSP exam now as an Associate of ISC2, or sit ISACA CISA and apply once your experience qualifies.
- Not sure: read ten job postings for the role you want next and count which certification they name.
FAQ
What is the difference between CISSP and CISA?
CISSP, from ISC2, is for people who build and lead security programs and tests risk-manager judgment across eight domains. ISACA CISA is for auditors who evaluate IT controls and tests auditor judgment across five domains, where the right answer preserves independence and reports rather than fixes.
Should I get Security+ or CISSP first?
Security+ first, for almost everyone. It has no experience requirement, while CISSP needs five years of security work to certify. Security+ can also count toward one of those years on ISC2's approved credential list.
Which is harder, CISSP or ISACA CISA?
It depends on your background. CISSP is broader and adaptive, with no going back. ISACA CISA is narrower but demands the counterintuitive auditor mindset. Both test judgment rather than recall.
Is the ISACA CISA passing score of 450 the same as 56 percent?
No. 450 is a scaled score on a 200 to 800 range, per ISACA, not a raw percentage. Aim for a clear margin on full-length practice rather than a percentage target.
Can I take CISSP or ISACA CISA without experience?
Yes. You can sit either exam first. A CISSP pass without experience makes you an Associate of ISC2, with six years to earn the five. For ISACA CISA, you apply for certification within five years of passing, once your experience qualifies.
Can I hold both CISSP and ISACA CISA?
Yes, and many senior security and audit professionals do. Most earn them years apart, starting with the one that fits their current role.
Is CISSP entry-level?
No. It is designed for experienced practitioners and managers and requires five years of paid security experience to certify.
Related on PrepClubs
- CISSP exam: format, domains, cost and difficulty: the complete CISSP guide.
- CISSP practice test and study plan: how to read BEST and FIRST questions.
- ISACA CISA practice questions: the auditor judgment the exam rewards.
- Security+ practice test: where most security careers start.
Practice the exam that fits your path
Each of these exams rewards a different kind of judgment, so your practice should match the one you are sitting. PrepClubs has a track for all three, each with a 25-question diagnostic and 10 full-length timed practice tests of original questions with a written rationale on every answer: CISSP (125 questions per test, weighted to the eight domains), ISACA CISA (150 questions per test) and Security+ (90 questions per test). Every track is backed by our Money-back Guarantee, and more than 3,700 students have prepared with PrepClubs. Practice at prepclubs.com/tests/cissp.
Practise for this exam
CISSP (Certified Information Systems Security Professional) practice tests
Full-length timed forms across every exam domain at the official weighting, with a clear rationale for every answer. Start with the 25-question diagnostic to see which domains need the most work.